Verify the OpenTune APK release identity first
Verification starts with identity, not with a scan result. OpenTune is an open-source Android music client maintained under the Arturo254 account. The repository, release tag and attached asset form one traceable chain. A page that uses the OpenTune name but links to another owner, a file host or a repacked installer is a different source until the upstream project confirms it.
The latest facts shown by this site are a dated reference. Open the tag, read the release notes and select the APK asset listed under that tag. GitHub source archives are not installable APKs, and a file named OpenTune.apk is not proof of provenance.
- Owner: Arturo254 on github.com
- Repository: Arturo254/OpenTune
- Current checked tag: 3.0.6
- Expected asset: app-universal-release.apk
- Android baseline in the project facts: Android 8.0 / API 26
| Fact to compare | Checked OpenTune value | Why it matters |
|---|---|---|
| Release owner | Arturo254/OpenTune | Separates the app from similarly named projects |
| Tag | 3.0.6 | Ties notes, source and assets to one snapshot |
| APK filename | app-universal-release.apk | Avoids selecting a ZIP, source archive or random variant |
| Package | com.Arturo254.opentune | Identifies the Android application installed on the device |
| File size | 26.78 MiB | A quick corruption or wrong-asset warning sign |
Check the filename, package name and Android requirements
Before opening the installer, compare the local file with the release asset. In the current reference record the filename is app-universal-release.apk and the size is 28,077,468 bytes, displayed as 26.78 MiB. A different filename can be legitimate in a newer release, but it must appear in the official asset list. Never repair a broken link by guessing a filename from an older version.
The package name is a second identity check after installation or when inspecting the APK. The current project value is com.Arturo254.opentune. Android 8.0 or later is required by the recorded minSdk 26 setting. If a download claims to be OpenTune but requests a different package, targets a different platform or offers an EXE, DMG or browser extension, stop and verify the publisher before continuing.
- Compare the full filename, including the .apk extension.
- Compare the byte size when the release page provides it.
- Check that the package is com.Arturo254.opentune after download.
- Confirm that the phone supports Android 8.0 or newer.
- Keep the release URL and tag in your notes for later support requests.
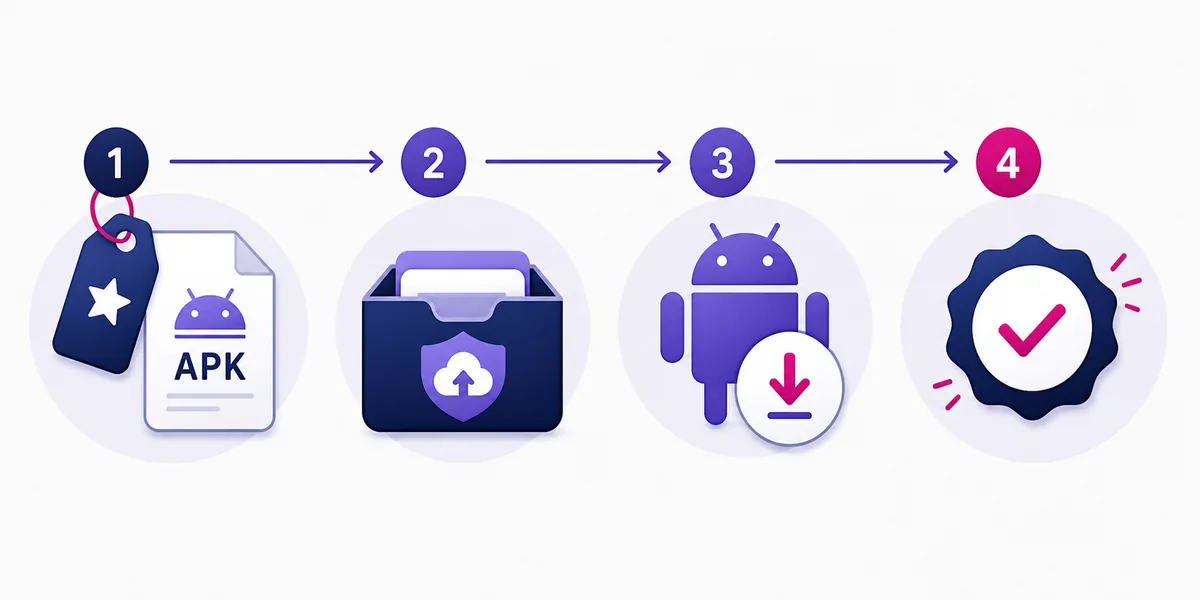
- Open the exact tag
Use the version link under Arturo254/OpenTune, not a third-party download directory.
- Select the APK asset
Choose the attached universal APK and avoid source code archives or unknown variants.
- Compare local facts
Check filename, size, version label and package name before allowing installation.
How to verify OpenTune APK with SHA-256
SHA-256 is a one-way digest of bytes. If even one byte changes, the resulting 64-character hexadecimal value changes. A digest comparison can show that your file matches a value published by a trusted source; it does not by itself prove that a random mirror is trustworthy. Copy the expected value from a release page or a project-controlled record, then calculate the digest locally without retyping or shortening it.
The current site record lists 1ae255fa1fb07c92bd1287ce9169b260bbbbdd47993a1211e37dbf8f0040c214 for the 3.0.6 APK. Treat this as a reference captured on August 13, 2026 and checked against the Releases page on November 5, 2026. If the upstream asset or digest changes, use the newer official value and record the date. A mismatch means stop: delete the file, download again from the release and investigate before installing.
- Windows PowerShell: Get-FileHash .\app-universal-release.apk -Algorithm SHA256
- macOS or Linux: shasum -a 256 app-universal-release.apk
- Compare all 64 hexadecimal characters, ignoring line wrapping only.
- Keep the command output beside the release URL and checked date.
- Never treat a green antivirus message as a replacement for provenance.
- Save the official expected digest
Copy it from the release facts you trust and label it with the exact tag and asset.
- Calculate the local digest
Run the platform command against the file you downloaded; do not hash a ZIP or a renamed copy.
- Compare without truncation
A single missing character or different case-sensitive value is a failed match.
- Record the result
Store the matched digest, source URL, filename and date so the check is auditable.
Check Android signing and the installed package
Android APKs are signed before installation. A signature check answers a different question from SHA-256: it helps compare the certificate used to sign an APK with a known publisher identity. The Proton verification guide used for the method explains the apksigner workflow and distinguishes the certificate digest from the APK file digest. OpenTune's public release page should remain the authority for the project identity; do not borrow another application's certificate value.
On a computer with Android SDK Build Tools, run apksigner verify --print-certs app-universal-release.apk. Read the signer certificate details and keep the output with the tag and package facts. On Android, an update that reports a signature conflict is a warning, not a reason to uninstall immediately. It can mean that the installed app came from another publisher or that the new asset is not the file you intended to use.
- Use apksigner from a trusted Android SDK Build Tools installation.
- Inspect certificate output for the exact APK you downloaded.
- Compare package and publisher together; one field alone is not enough.
- Treat an update signature conflict as a source investigation.
- Back up app data before any uninstall or downgrade decision.
- Install or locate apksigner
Android Studio users can find it in the SDK build-tools directory.
- Print the certificate
Use apksigner verify --print-certs and point it at the exact APK path.
- Compare known evidence
Use a publisher certificate reference only when the project publishes one for that release.
- Resolve conflicts carefully
Do not remove a working installation until the package, source and backup situation are clear.
| Check | What it can establish | What it cannot establish |
|---|---|---|
| Filename and size | You selected the expected release asset | That a mirror is the publisher |
| SHA-256 | Bytes match a trusted published digest | That the code is harmless |
| APK certificate | The signing identity matches a known reference | That the download page was official |
| Package name | The installed application ID | The app's privacy or behavior |
| Release URL | Where the publisher attached the asset | A future release will keep the same facts |
Red flags that should stop an OpenTune APK check
Stop when a page asks you to disable security controls, upload a private APK or sign in before showing the source. A countdown can be an advertising wrapper; the final host and asset should still be visible on the official release record. Be cautious with promises that a file is 100% safe or officially sponsored.
- The owner is not Arturo254 or the repository name is misspelled.
- The page offers an EXE, DMG, DEB or modified APK that the release does not list.
- The filename, package or size differs without a release note explaining it.
- The SHA-256 value is shortened, missing or copied from another app.
A repeatable verification checklist
- Source and tag are visible on GitHub.
- Asset is an APK attached to that tag.
- Filename, byte size and package are consistent.
- SHA-256 matches a dated trusted reference.
- Certificate output is recorded when a signature check is required.
- A backup exists before downgrade, uninstall or data reset.
- Install only after a match
If any identity or digest check fails, stop and obtain a fresh official asset.
- Recheck after updates
New tag or asset changes facts; never reuse an old digest blindly.
Sources used for this verification guide
- Arturo254/OpenTune Releases - Official release tags, notes and attached APK assets.
- Arturo254/OpenTune source repository - Canonical Android project identity and source context.
- How to verify Proton APKs - First-party example of SHA-256 and apksigner certificate verification; method reference only.
Verify OpenTune APK FAQ
What is the official OpenTune APK source?
Use the Arturo254/OpenTune repository and its GitHub Releases page. This site links to those first-party pages and does not mirror the APK.
What package name should OpenTune use?
The current reference record lists com.Arturo254.opentune. A different package is not automatically wrong, but it needs an explicit upstream explanation before installation.
What SHA-256 value is listed for OpenTune 3.0.6?
The dated site record lists 1ae255fa1fb07c92bd1287ce9169b260bbbbdd47993a1211e37dbf8f0040c214 for app-universal-release.apk. Recheck the official release before relying on it because release facts can change.
Does a matching hash prove that an APK is safe?
No. It proves that the bytes match the published reference. You still need a trustworthy source, signature context, sensible permissions and your own device policy.
Why does Android report a signature conflict?
The installed app and the new APK may come from different publishers or signing keys. Keep the current installation, compare sources and back up data before considering removal.
Can I verify an APK on Windows or Linux?
Yes. Use Get-FileHash or shasum for SHA-256, and use apksigner from Android SDK Build Tools when you need certificate details.